WordPress Website Security Audit
A WordPress-specific security audit — plugins, themes, core, users, malware and hardening, with a clear remediation roadmap.
Explore MoreYour website is an important part of your business. Security weaknesses can expose sensitive information, disrupt operations, and damage customer trust. ZyvenTech helps identify potential website security risks through a structured security audit tailored to your website's technology, features, and requirements.
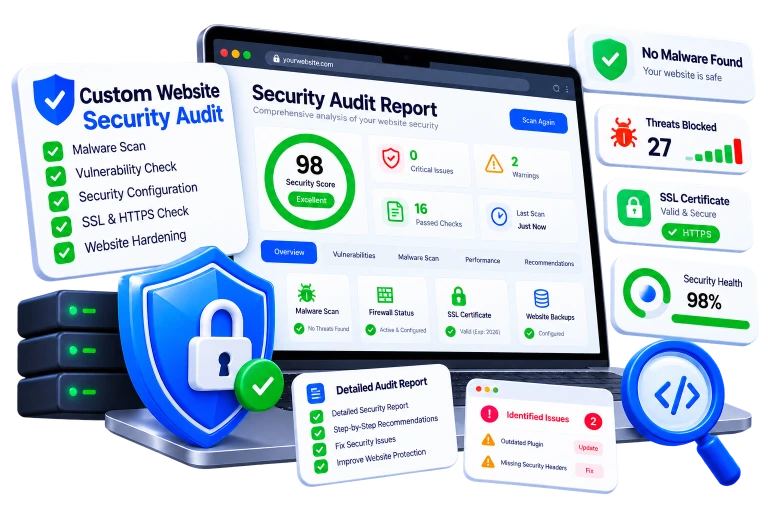
Most website breaches exploit known, preventable weaknesses: outdated components, weak access control, missing security headers, exposed files. A structured audit finds these issues while they are still cheap to fix.
We audit custom-coded websites across technology stacks, checking the areas attackers actually probe — and we report findings by severity, with clear remediation steps for each one.
From vulnerability assessment and access controls to data privacy checks and remediation guidance.
Review your website for potential security weaknesses, outdated components, unsafe configurations, and other issues that may increase risk.
Examine relevant server, application, HTTPS, and security-related settings to identify misconfigurations and opportunities for improvement.
Assess login mechanisms, password policies, user roles, permissions, and access restrictions to identify potential weaknesses.
Review how your website handles sensitive information, form submissions, and data transmission, based on the application's architecture and scope.
Check for indicators of malicious code, suspicious files, unexpected changes, and other signs of possible compromise using appropriate tools and methods.
Assess relevant API endpoints and website forms for common security issues, including insufficient validation, excessive data exposure, and inappropriate access controls.
Review HTTPS implementation and relevant certificate and transport security settings to identify potential configuration issues.
Receive a prioritized report outlining identified findings, their potential impact, and recommended corrective actions.
A structured 8-step methodology to assess, validate, prioritize, and remediate website vulnerabilities.
We understand your website, technology stack, business requirements, and audit objectives. Testing boundaries and written authorization are confirmed before assessment begins.
We review the website's architecture, framework, CMS, integrations, exposed services, and relevant components within the approved scope.
We examine relevant HTTPS settings, security headers, application configuration, access restrictions, and other security controls.
We use appropriate assessment techniques to identify potential weaknesses in the website and its components, staying within the agreed testing scope.
We assess relevant login flows, permissions, session handling, input validation, and sensitive data exposure.
We validate potential findings where practical, assess their likely impact, and prioritize them based on severity and business risk.
We prepare a clear report containing the findings, supporting evidence where appropriate, risk priorities, and recommended remediation steps.
Where included in the agreed scope, we review implemented fixes and perform follow-up checks to determine whether identified issues have been addressed.
Industry methodologies and security controls we follow to audit and harden custom web applications.
*Assessments are customized according to your web application's architecture, programming framework, and hosting environment.
A security audit helps you understand where your website may be vulnerable and what actions can reduce risk.
*An audit can reduce uncertainty and help improve security, but it cannot guarantee that a website is completely secure or free from vulnerabilities.
The final deliverables depend on the website's architecture, access provided, testing scope, and selected service package.
A website security audit is a structured review of a website's security controls, configuration, and potential vulnerabilities. It helps identify weaknesses and recommend practical improvements.
The assessment can be tailored to custom-built websites, business websites, web applications, and other supported platforms. The audit scope depends on the website's technology and requirements.
We plan assessments carefully to minimize disruption. Any testing that could affect availability or data requires explicit approval and appropriate safeguards. Where practical, testing may be conducted in a staging environment.
The audit includes recommendations for addressing identified issues. Remediation can be discussed separately or included if agreed as part of the project.
The timeline depends on the website's size, complexity, technology, access arrangements, and depth of assessment.
Yes. The agreed deliverables can include a report describing findings, their potential impact, severity priorities, and recommended remediation steps.
We can discuss an appropriate assessment to investigate possible indicators of compromise. Incident response and malware cleanup may require a separate scope, depending on the situation.
No audit can guarantee complete security. The objective is to identify relevant weaknesses, provide actionable recommendations, and help improve your website's security posture.
A WordPress-specific security audit — plugins, themes, core, users, malware and hardening, with a clear remediation roadmap.
Explore MoreCustom-coded websites built around your business goals — fast, responsive, secure and designed to convert visitors into enquiries.
Explore MoreScalable web and mobile applications built with modern architectures, robust data protection and intuitive user experiences.
Explore MoreUnderstand your website's security risks with a structured assessment tailored to your technology and business needs. ZyvenTech can help you identify potential weaknesses, prioritize fixes, and plan your next security improvements. Let's discuss your website and determine the right audit scope.